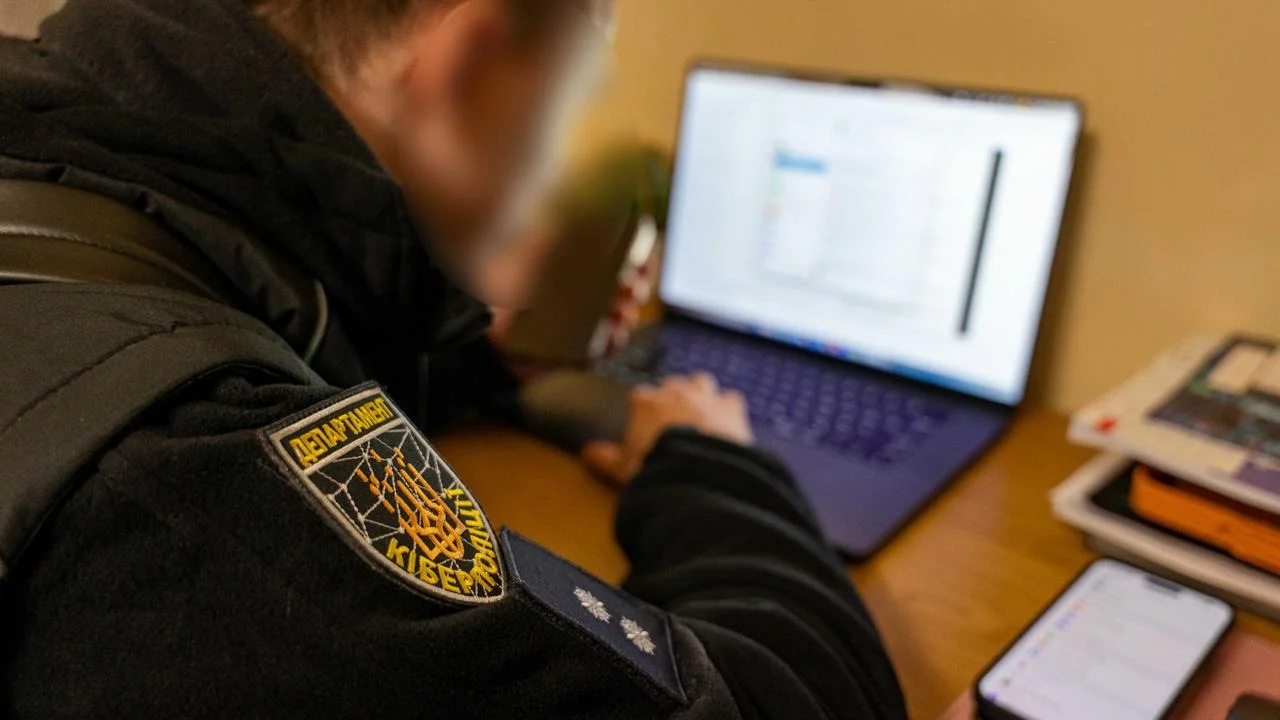
Over $40.5 million extorted from 28 companies: National Police, in collaboration with FBI, have exposed group of hackers, – Tsutsikiridze. PHOTOS
An international hacking group, which attacked companies and demanded ransoms in exchange for restoring access to data, has received over $40.5 million from at least 28 businesses. Four key members were arrested in Ukraine as part of a joint investigation by the National Police and the FBI.
Maksym Tsutsikiridze, acting head of the National Police of Ukraine, provided details of the joint investigation with the FBI in an exclusive interview with Censor.NET.
What is known?
An employee of the company spoke on the phone with a supposed IT support specialist. Whilst one of the attackers kept him on the line, the other gained access to the corporate system. The conversation only ended after confirmation that the hack had been successful.
This is one of the documented incidents involving an international hacking group that stole data, disrupted business operations and demanded ransoms running into millions.
Among the victims was an American company, which paid the hackers five million dollars following the attack.
"The attackers stole 1.4 terabytes of data from the American company and extended the attack to other companies in the same group. Initially, they demanded $10 million. Following negotiations, they received $5 million," he said.
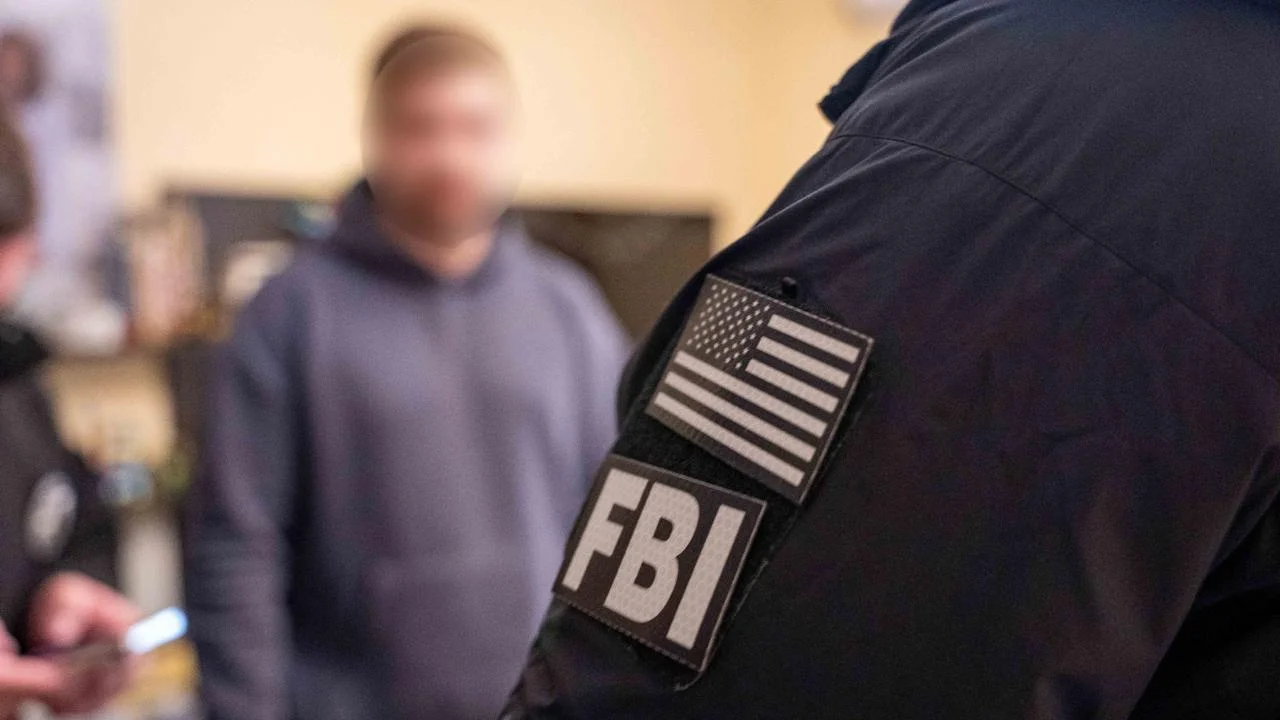
The organisation’s activities had been documented for over two years by operatives from the Cyberpolice Department and investigators from the Main Investigation Directorate, in collaboration with the US Federal Bureau of Investigation.
"We have identified at least 28 companies that paid the hackers over $40.5 million in ransoms – the equivalent of around 1.8 billion hryvnias. This is the money that has already been paid. We are still determining the final amount of the losses," noted Tsutsikiridze.
According to the investigation, the organisation comprises at least 27 individuals from various countries, including Ukraine, Kazakhstan and Russia. A wider criminal network linked to it comprises over 60 members across eight jurisdictions. Among them are former members of the notorious Conti hacking group.
How was the attack carried out?
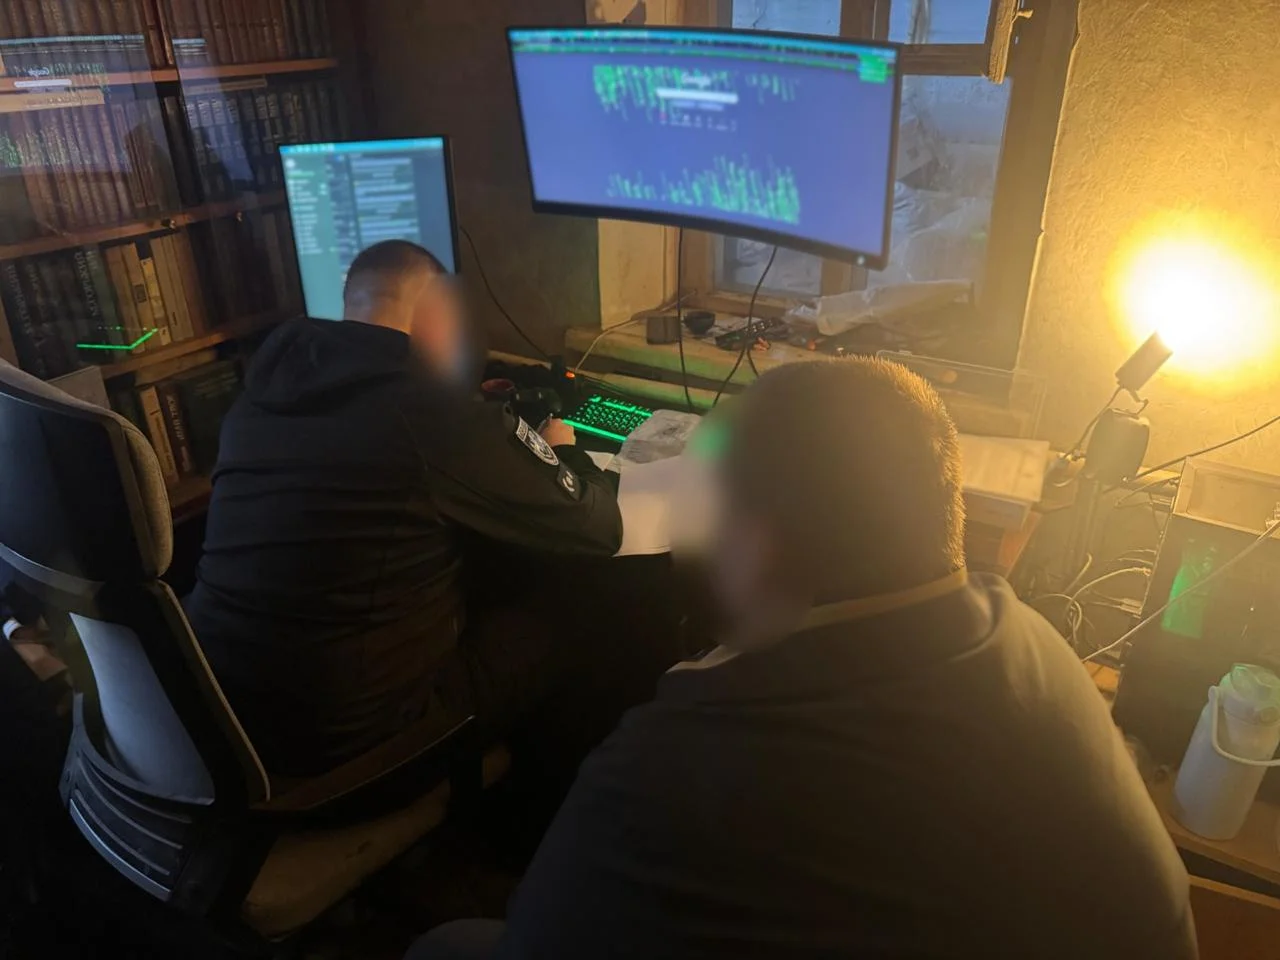
Each attack was meticulously planned. The attackers studied the company’s financial situation, its assets, staff and the vulnerabilities of its information systems. Their targets included companies in the oil and gas, pharmaceutical, industrial and logistics sectors, as well as financial institutions and critical infrastructure facilities.
They used deception to gain access to corporate networks. According to the head of the National Police, the group developed its own tool to automate such contacts.
"They created their own platform with voice messages generated by artificial intelligence. They telephoned company employees, introducing themselves as IT support specialists. Under the pretext of providing technical assistance, they persuaded them to hand over login details or install remote access software. This is how they gained access to the corporate network," said Tsutsikiridze.
Once inside, the hackers stole confidential information and encrypted files, in particular using ransomware. The companies’ operations were paralysed.
"The companies were denied access to their own data, and then the hackers demanded millions to decrypt it. At the same time, they threatened to publish the stolen information. The victims were put under pressure from both sides, forcing them to pay the ransom in cryptocurrency," he explained.
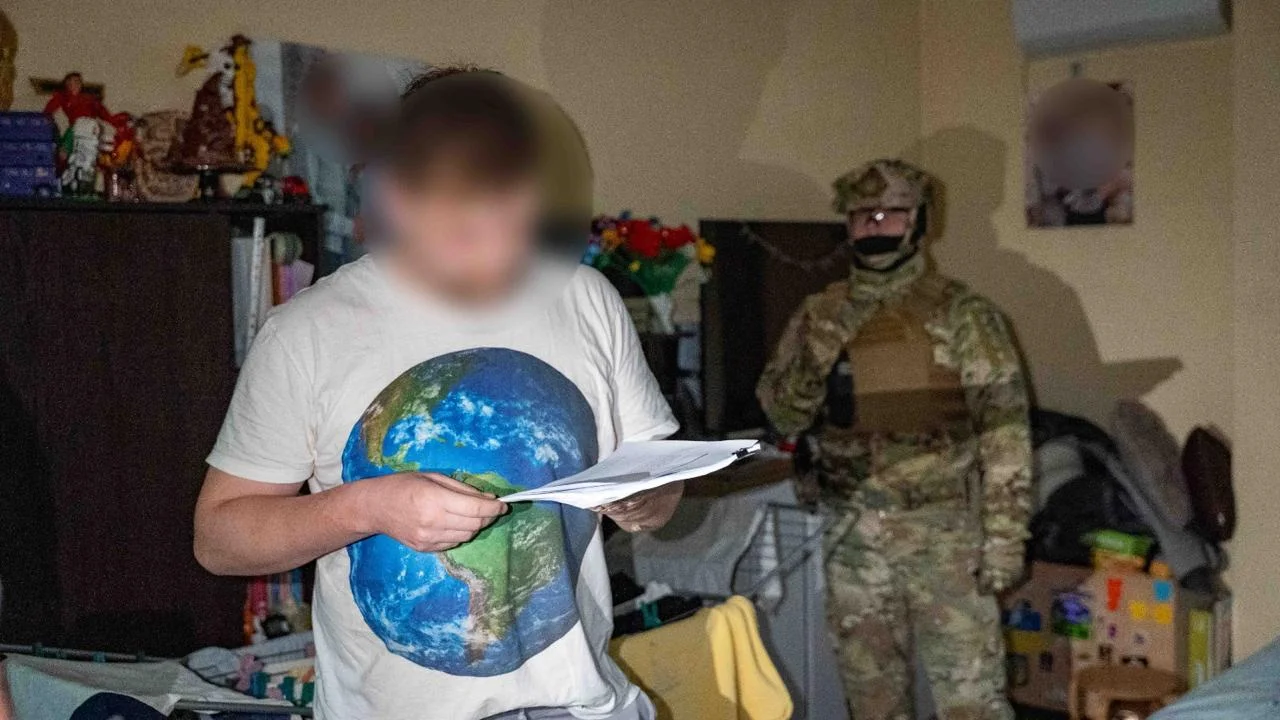
As part of an international operation, police officers, under the procedural guidance of the Office of the Prosecutor General, carried out 66 simultaneous raids in Kyiv and 11 regions of Ukraine. Representatives of US law enforcement agencies were involved in the operation. Special forces, including TacTeam in Kyiv, provided security support.
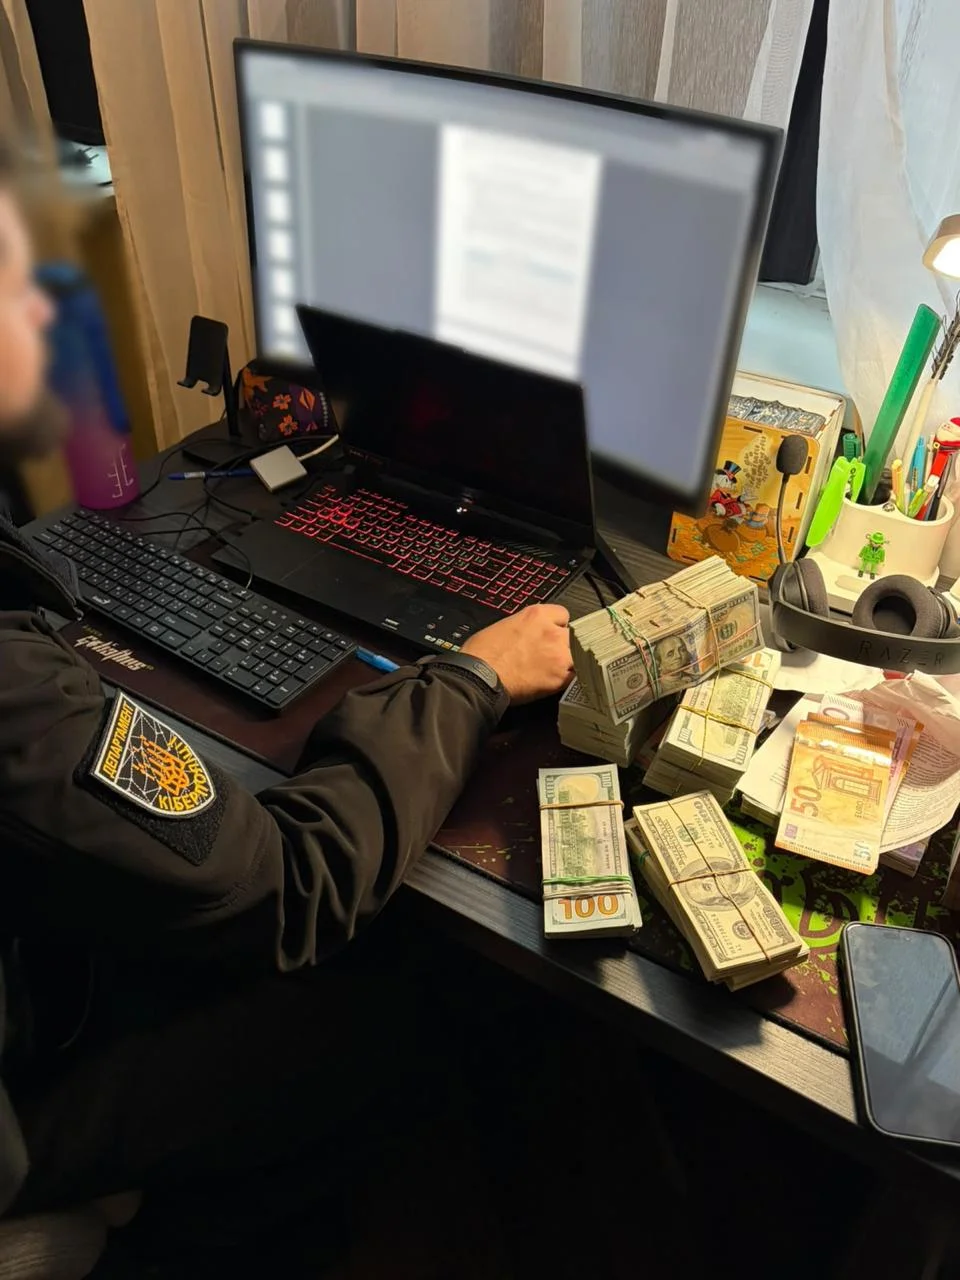
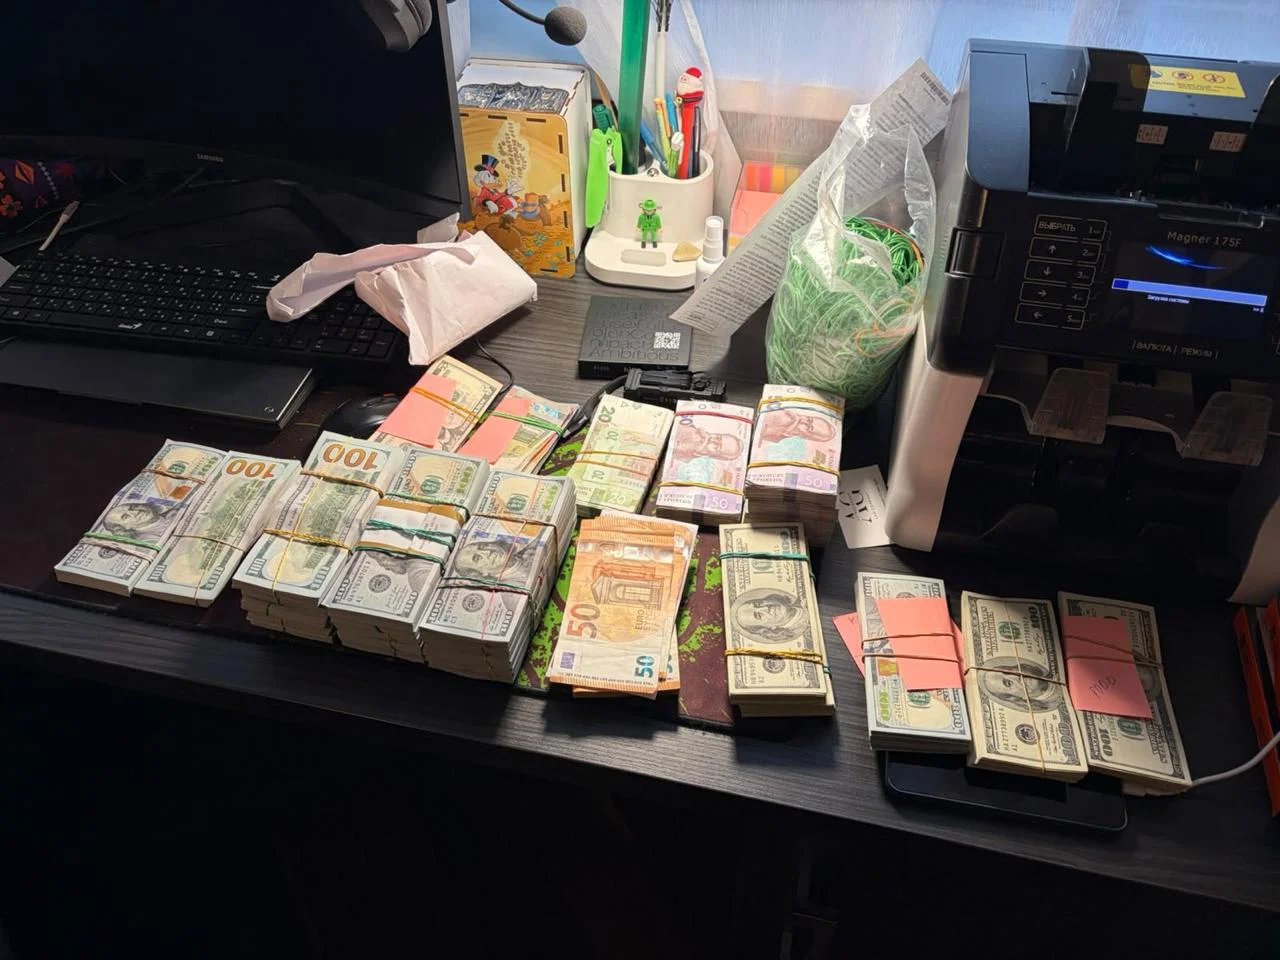
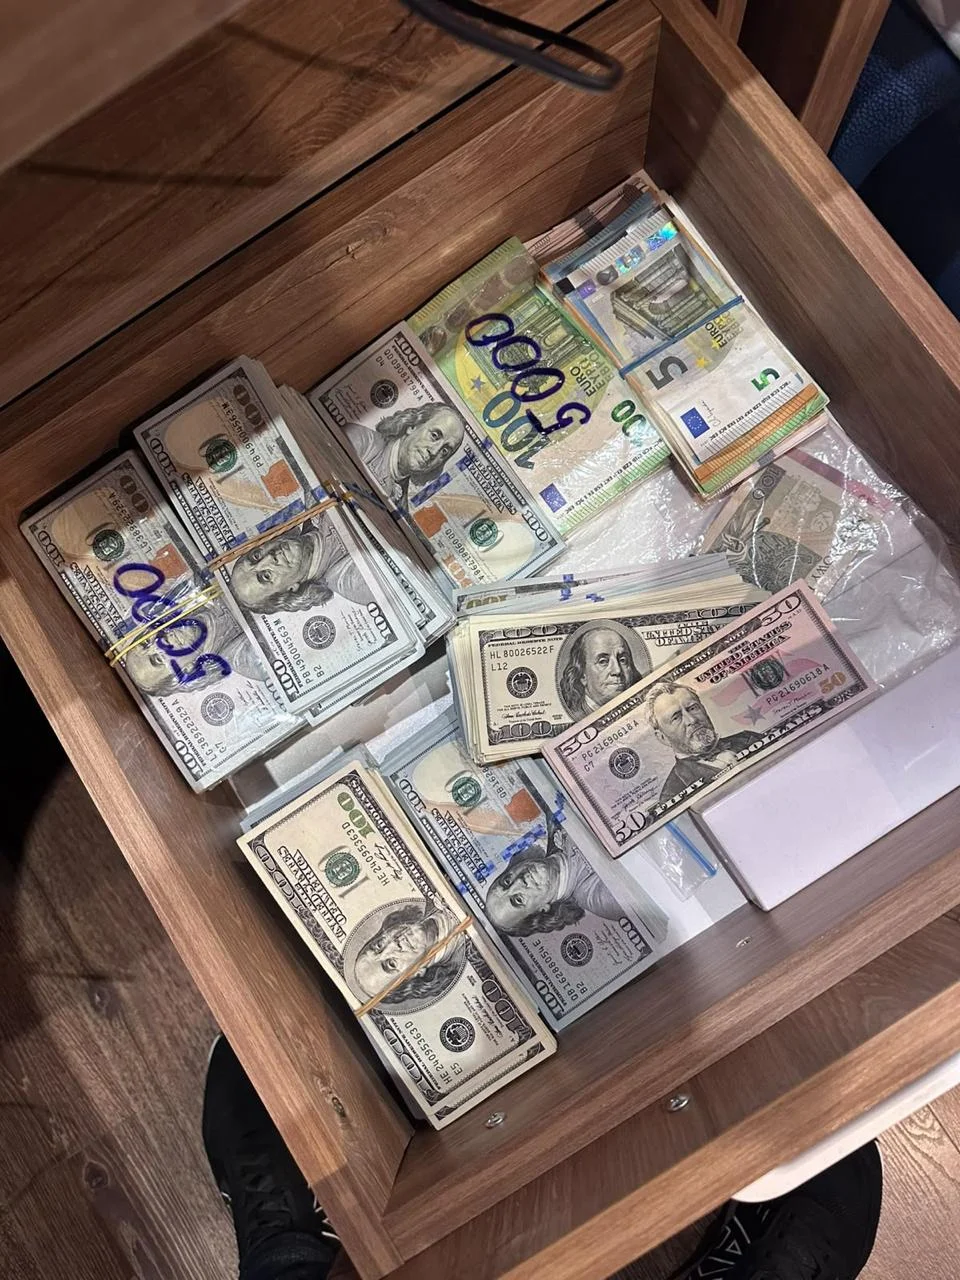
Computer equipment, mobile phones, bank cards, nearly 370,000 dollars and 20,000 euros in cash were seized.
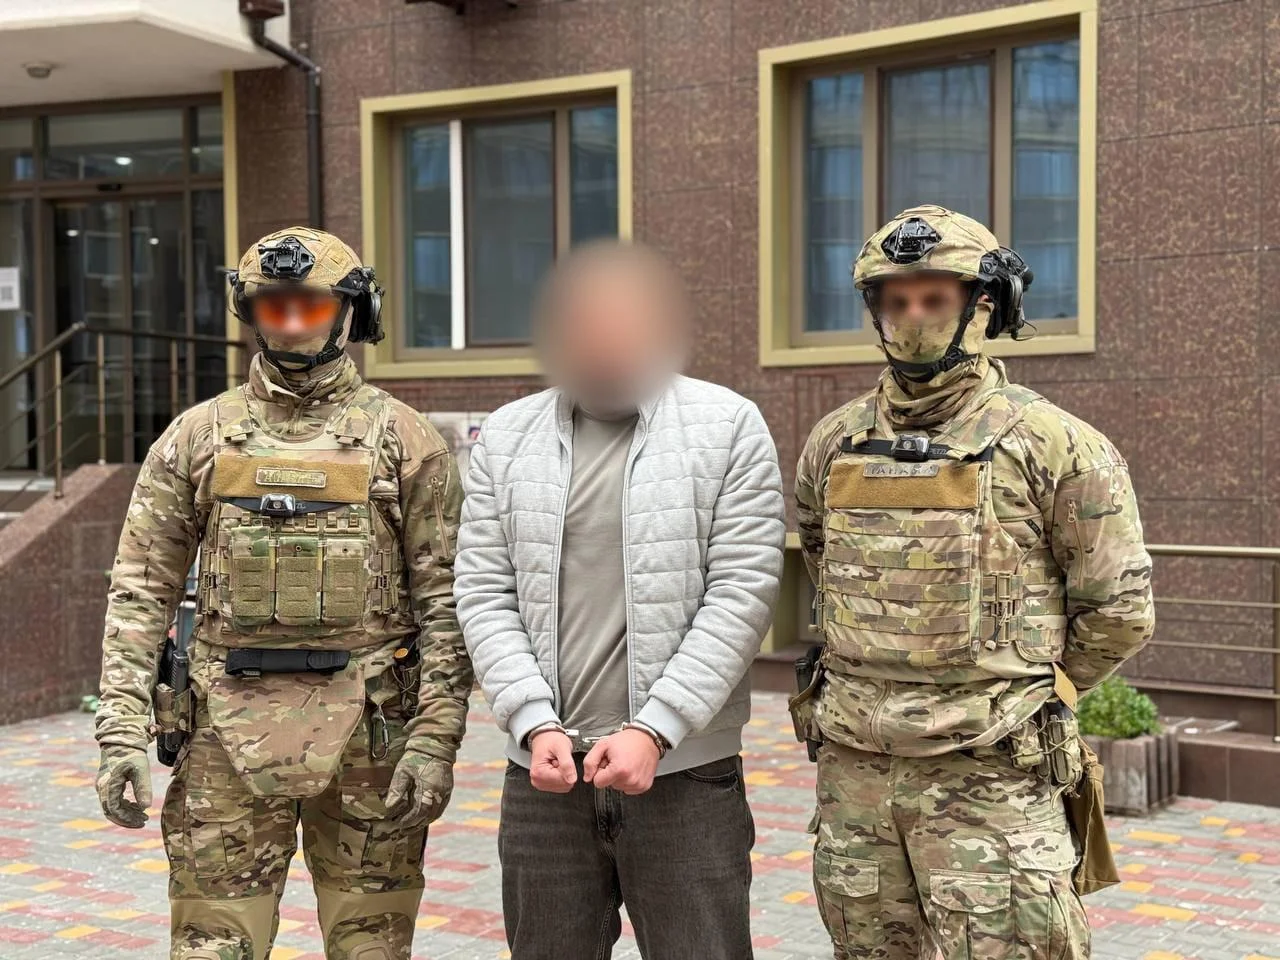
"Four key members of the group have been served with notices of suspicion. All four are in custody. We are continuing to identify other members of the international network and their involvement in the attacks," said Tsutsikiridze.
The charges relate to participation in a criminal organisation and unauthorised interference with information systems – Part 2 of Article 255 and Part 5 of Article 361 of the Criminal Code of Ukraine. The suspects face up to 15 years’ imprisonment.